Cybersecurity analysts play a crucial role in protecting organizations from cyber threats. They are responsible for monitoring networks, identifying vulnerabilities, and responding to security incidents. If you enjoy problem-solving, analyzing data, and staying ahead of evolving cyber threats, this could be the right career for you.
The demand for cybersecurity analysts is growing rapidly as businesses and governments face increasing cyber risks. Organizations need professionals who can safeguard sensitive data, detect threats, and prevent security breaches.
Salary expectations vary based on experience and location.
In the United States, entry-level cybersecurity analysts can expect to earn between $60,000 and $80,000 per year.
Mid-level professionals typically earn between $90,000 and $110,000, while senior-level cybersecurity analysts and specialists can earn $120,000 or more.
The cybersecurity industry offers strong job security and career growth. According to industry reports, there are millions of unfilled cybersecurity positions worldwide, with demand continuing to rise.
This guide is designed for beginners, career switchers, and IT professionals looking to enter the field. It provides insights into essential skills, certifications, career paths, and industry expectations to help you make an informed decision about becoming a cybersecurity analyst.
Understanding the Role of a Cybersecurity Analyst
Cybersecurity analysts are responsible for monitoring, detecting, and responding to security threats. Their primary goal is to protect an organization’s digital assets from cyberattacks. They analyze security data, investigate incidents, and recommend improvements to security policies and systems.
The day-to-day responsibilities of a cybersecurity analyst include monitoring network traffic for suspicious activity, analyzing security alerts, responding to incidents, performing vulnerability assessments, and ensuring compliance with security policies. They also collaborate with IT teams to implement security measures and educate employees on cybersecurity best practices.
Cybersecurity analysts work in various industries, including finance, healthcare, government, technology, and retail. Any organization that handles sensitive data needs security professionals to protect against cyber threats.
The role of a cybersecurity analyst differs from other cybersecurity positions. A security operations center (SOC) analyst focuses on real-time monitoring and incident response.
A penetration tester, also known as an ethical hacker, simulates cyberattacks to identify vulnerabilities.
A security engineer designs and implements security systems to protect an organization’s infrastructure. While these roles overlap, a cybersecurity analyst typically works across multiple areas of security operations, making it an excellent starting point for a cybersecurity career.
Skills Required to Become a Cybersecurity Analyst
A successful cybersecurity analyst needs a combination of technical and soft skills. Technical skills help in identifying and mitigating cyber threats, while soft skills ensure effective communication and problem-solving in high-pressure situations.
Technical skills include knowledge of networking fundamentals, such as TCP/IP, DNS, and firewalls, to understand how data flows across networks and identify suspicious activity.
System administration experience in Windows and Linux is essential for managing security configurations and troubleshooting security incidents.
Familiarity with security tools such as Security Information and Event Management (SIEM) systems, Intrusion Detection and Prevention Systems (IDS/IPS), and endpoint security solutions is critical for monitoring and responding to threats.
Understanding threat intelligence and analysis helps cybersecurity analysts anticipate potential attacks and take proactive measures. Knowledge of incident response and digital forensics is also important for investigating security breaches and mitigating their impact.
Soft skills play a crucial role in cybersecurity. Analytical thinking allows professionals to detect patterns and anomalies in security data.
Problem-solving skills help in developing effective solutions to security issues.
Strong communication skills are necessary for explaining security risks and mitigation strategies to non-technical stakeholders. Attention to detail ensures that potential threats are not overlooked and that security policies are correctly implemented.
Cybersecurity Analyst Education & Certifications
There are multiple pathways to becoming a cybersecurity analyst, and education requirements vary based on employer expectations. Some companies require a formal degree, while others accept self-study and certification-based learning.
A formal degree in cybersecurity, computer science, or information technology can provide a structured learning path and make candidates more competitive. However, self-study and online courses can also be effective for those who prefer a flexible approach. Many cybersecurity professionals enter the field through bootcamps, online training programs, and hands-on experience rather than a traditional college education.
Certifications can significantly enhance career prospects.
The CompTIA Security+ certification is an entry-level credential that covers fundamental cybersecurity concepts and is widely recognized by employers.
The Certified Ethical Hacker (CEH) certification focuses on ethical hacking and penetration testing skills, making it valuable for those interested in offensive security.
The GIAC Security Essentials (GSEC) certification provides a deeper understanding of cybersecurity principles and best practices.
The Certified Information Systems Security Professional (CISSP) certification is an advanced credential that validates expertise in designing and managing security programs.
The Certified SOC Analyst (CSA) certification is ideal for those who want to specialize in security operations and incident response.
Choosing the right certification depends on career goals and experience level. Beginners should start with foundational certifications like Security+ before progressing to more specialized credentials.
Those interested in ethical hacking can pursue CEH, while professionals aiming for leadership roles should consider CISSP. Continuous learning and obtaining relevant certifications will help cybersecurity analysts stay competitive in this evolving field.
Gaining Hands-On Experience
Practical experience is crucial for becoming a cybersecurity analyst. Employers value candidates who can demonstrate hands-on skills in real-world scenarios. Setting up a home lab is an excellent way to practice cybersecurity concepts. Using virtual machines, open-source security tools, and simulated attacks, aspiring analysts can learn how to detect and mitigate threats in a controlled environment.
Online platforms offer free cybersecurity training, including hands-on labs and exercises. Capture the Flag (CTF) competitions provide an opportunity to solve security challenges, test penetration testing skills, and improve problem-solving abilities. Engaging in these activities helps build technical expertise and makes candidates more attractive to employers.
Internships and volunteer cybersecurity projects can also provide valuable experience. Many organizations, including nonprofits and startups, need security assistance but may lack the budget for full-time professionals. Volunteering for security audits, compliance checks, or risk assessments can help build practical knowledge and establish credibility in the field.
Freelancing is another effective way to gain hands-on experience. Platforms like Upwork and Fiverr allow aspiring analysts to take on small security projects, even if they start at lower rates. Performing security assessments, vulnerability scans, and compliance audits for clients can provide real-world experience while also building a portfolio. As skills improve, freelancers can gradually increase their rates and transition into higher-paying roles.
How to Land Your First Cybersecurity Analyst Job
Securing a cybersecurity analyst job requires a combination of skills, certifications, and networking. A well-crafted resume and cover letter can help candidates stand out. Emphasizing hands-on experience, relevant certifications, and security-related projects is essential. Providing links to personal projects, GitHub repositories, or write-ups of CTF challenges can further showcase expertise.
Cybersecurity analyst job opportunities can be found on job boards, LinkedIn, and government websites. Networking with industry professionals through conferences, meetups, and online forums can open doors to new opportunities. Engaging with cybersecurity communities and seeking mentorship from experienced professionals can provide guidance and referrals.
Preparing for technical and behavioral interviews is also important. Employers assess candidates' ability to analyze security incidents, respond to hypothetical threats, and explain complex concepts in simple terms. Practicing common security scenarios and reviewing past cybersecurity incidents can help candidates perform well in interviews.
Building a portfolio of cybersecurity projects demonstrates practical skills and problem-solving abilities. Documenting security assessments, penetration testing reports, and security research projects can make a strong impression on potential employers.
With persistence, continuous learning, and hands-on practice, aspiring cybersecurity analysts can successfully land their first job and begin a rewarding career in cybersecurity.
Cyber Analyst Career Growth & Specializations
Cybersecurity analysts have multiple career paths depending on their skills, interests, and experience. Many professionals start in Security Operations Centers (SOC) as SOC analysts, monitoring threats in real time. From there, they may transition into security engineering, designing and implementing security controls, or move toward cybersecurity architecture, creating large-scale security frameworks for enterprises.
incident response and digital forensics, where analysts investigate breaches, track cybercriminal activities, and recover compromised data. Those with an interest in governance, risk, and compliance (GRC) often become compliance analysts, working to ensure organizations follow security regulations. Over time, these professionals can advance into risk management, security leadership, and CISO (Chief Information Security Officer) roles
Some cybersecurity analysts choose to specialize in penetration testing, focusing on offensive security, or cloud security, securing cloud infrastructures as more businesses move to cloud-based environments. Each specialization requires continuous learning, advanced certifications, and hands-on experience.
Certifications such as CISSP, OSCP (Offensive Security Certified Professional), and CCSP (Certified Cloud Security Professional) can help analysts transition into specialized roles.
Tools and Technologies Used by Cybersecurity Analysts
Cybersecurity analysts rely on various tools to detect, prevent, and respond to security incidents. Commonly used solutions include SIEM (Security Information and Event Management) platforms like Splunk, QRadar, or ArcSight; endpoint security tools such as CrowdStrike, SentinelOne, and Microsoft Defender; and vulnerability scanners like Nessus or OpenVAS to pinpoint weaknesses.
Firewalls and IDS/IPS (Intrusion Detection and Prevention Systems) help filter malicious traffic and detect potential attacks, while packet analysis tools like Wireshark allow deeper inspection of network traffic and investigations into suspicious activity.
Mastering these tools is essential for building a solid foundation in network defense.
Challenges and Realities of the Job
Though cybersecurity is an exciting and rewarding field, it comes with challenges.
The high-pressure environment can involve real-time threat response, requiring quick decision-making. Long hours and unpredictable workloads are common, since security incidents can happen at any time.
Cyber threats constantly evolve, so analysts must keep learning to stay effective.
Stress and burnout are concerns, given the high stakes and ongoing vigilance required.
Additionally, many people think cybersecurity is all about hacking, but much of the job involves risk assessment, compliance, and monitoring rather than active exploitation.
Mistakes to Avoid
Focusing too heavily on certifications without gaining practical experience can limit career growth. Hands-on skills acquired through home labs, internships, and freelancing often matter as much as formal credentials.
Ignoring soft skills like communication and problem-solving can also be detrimental, as these abilities are vital when collaborating with colleagues or explaining security concerns to non-technical stakeholders.
Failing to network with industry professionals may mean missing out on job referrals and mentorship opportunities.
Overlooking foundational IT knowledge—such as networking, system administration, and scripting—can make it harder to grasp complex security concepts. Finally, burning out by pushing too hard too soon is a frequent pitfall, so balancing hard work with self-care is crucial for long-term success.
Conclusion
A career as a cybersecurity analyst offers exciting opportunities, strong job security, and the chance to protect organizations from evolving cyber threats. Whether you're just starting out, transitioning from another field, or looking to specialize, the cybersecurity industry provides a clear path for growth and continuous learning.
Success in this field requires a mix of technical expertise, problem-solving skills, and hands-on experience. Certifications and education can open doors, but real-world experience—whether through home labs, freelancing, internships, or CTF competitions—is what sets professionals apart.
As cyber threats become more sophisticated and widespread, the demand for skilled cybersecurity analysts will only grow. Staying curious, adaptable, and proactive in learning new technologies and security trends will ensure long-term success in this field.
Cybersecurity is more than just a job—it’s a mission to defend, protect, and secure the digital world. If you’re ready to embark on this journey, start building your skills today, connect with industry professionals, and take advantage of the countless opportunities waiting for you.
Your future in cybersecurity begins now!
About the Author
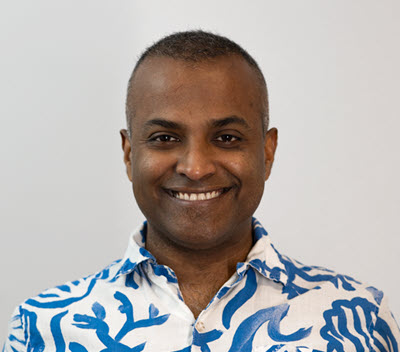
Specializing in areas like cloud security, compliance, and incident response, Nandy has worked with high-profile clients, including Microsoft, Dell, NASA, Department of Defense, National Cybersecurity Department, National Polytechnic in New Zealand, and Fortune 500 companies, helping them navigate complex security challenges with tailored solutions.
After transitioning from a corporate 9-5 cybersecurity job to freelancing, he quickly became a Top Rated Plus cybersecurity freelancer on Upwork, providing consulting to 200+ clients worldwide and earning close to $1 million in just a few short years.
Recognized as one of Upwork’s Top Rated Plus freelancers—an elite designation held by less than 1% of the 18,000,000+ freelancers on the platform—Nandy is celebrated for his hands-on expertise and results-driven approach.
From cutting response times with Azure Sentinel to achieving 90% reductions in phishing success rates, his projects consistently deliver measurable outcomes that protect businesses and build trust.
Nandy has secured over $2.3 billion in financial transactions, protecting enterprise clients from fraud, breaches, and insider threats.
He has played a crucial role in fortifying Fortune 500 companies and government agencies, ensuring zero data leaks and maintaining airtight compliance with global regulations.
His expertise extends to shaping Microsoft security solutions, having worked alongside Microsoft’s engineering teams on Intune, Defender, and Copilot. His direct contributions have influenced key security features used by millions of users worldwide.
Nandy’s impact is reflected in his results. He successfully eliminated 99% of cyber threats for a Department of Defense contractor by implementing an advanced security framework that set a new benchmark for future projects.
He led security optimization for a national government initiative, achieving 100% compliance and securing critical infrastructure against cyber warfare threats.
His forensic analysis and strategic security overhauls have prevented multi-million dollar breaches, safeguarding organizations at scale.
With over 10,000 consulting hours, 200+ high-impact projects, and a 100% Job Success Rate, Nandy continues to deliver top-tier cybersecurity solutions that protect businesses worldwide.
As the CEO of Cyber Swiss Army Knife Squad, Nandy leads cutting-edge initiatives that enhance client security and compliance. He’s also passionate about sharing his knowledge with aspiring freelancers, offering actionable strategies to help them succeed in their own careers.
Over the years, Nandy gained extensive experience mentoring and training professionals in cybersecurity, compliance, and incident response. His focus has been on helping individuals transition into cybersecurity careers, improving technical skills, and guiding freelance consultants toward long-term success. Nandy has conducted training sessions, webinars, and 1-on-1 coaching for professionals at various career stages.
Additionally, he has hands-on teaching experience at Level 7, where he instructed students on networking, security, and building server environments. Nandy provided one-on-one guidance, helping students shape their careers by demonstrating practical, real-world applications and hands-on implementations of cybersecurity concepts.
Nandy’s mission is to help the next generation of cybersecurity professionals to effectively combat cybercrime, prevent costly cyberattacks that harm businesses worldwide, and build sustainable, impactful careers in cybersecurity and beyond.
His courses are available on Udemy, SkillShare, and other major learning platforms.
Nandy's first published book, Master Upwork: Achieve Financial Freedom Through a Freelance Cybersecurity Career, was hailed as "groundbreaking" and featured by Fox 40, HTV Channel 10, the Globe and Mail, News Channel Nebraska, the Chronicle Journal, the Daily Times Leader, and 98.3 FM Radio.
Education and Certifications:
- BASc in Computer Science from Cornell University
- CompTIA Security+ Certification
- CompTIA Security+ CE Certification
- Microsoft Certified Professional
- Project Management Professional (PMP)
- Certified Information Security Manager
- Microsoft Certified: Security Operations Analyst Associate
- Microsoft Certified: Identity and Access Administrator Associate
- Microsoft Certified: Azure Security Engineer Associate
- Microsoft 365 Certified: Security Administrator Associate
- Microsoft 365 Mobility and Security
- Microsoft 365 Certified: Enterprise Administrator Expert
- Microsoft Certified: Azure Solutions Architect Expert
- Microsoft Azure Architect Technologies
- Microsoft Azure Architect Design
- Microsoft Certified Trainer 2021-2022
- Microsoft 365 Identity and Services
- ITIL® 4 Foundation CPD
You can learn more about Nandy and access free learning resources on his website NandyCyberSuccess.com or follow him on LinkedIn for industry news and updates.
References
McKinsey & Company. (2022). New survey reveals $2 trillion market opportunity for cybersecurity technology and service providers. https://www.mckinsey.com/capabilities/risk-and-resilience/our-insights/cybersecurity/new-survey-reveals-2-trillion-dollar-market-opportunity-for-cybersecurity-technology-and-service-providers
Cybersecurity Ventures. (2020). Cybercrime to cost the world $10.5 trillion annually by 2025. https://cybersecurityventures.com/cybercrime-damages-6-trillion-by-2021/ FBI IC3. (2023). 2023 Internet Crime Report. https://www.ic3.gov/AnnualReport/Reports/2023_ic3report.pdf IBM. (2024).
Cost of a Data Breach Report. https://www.ibm.com/reports/data-breach Proofpoint. (2024). FBI's IC3 Report: Losses from Cybercrime Surpass $12.5 Billion—a New Record. https://www.proofpoint.com/us/blog/email-and-cloud-threats/fbis-ic3-report-losses-cybercrime-surpass-125-billion-new-record UpGuard. (2024).
What is the Cost of a Data Breach in 2024? https://www.upguard.com/blog/cost-of-a-data-breach-2024 Verizon. (2024). 2024 Data Breach Investigations Report. https://www.verizon.com/business/resources/reports/dbir/
Bitdefender. (2024). Marriott data breach costs. https://www.bitdefender.com/en-us/blog/hotforsecurity/marriott-data-breach-cost-the-hotel-chain-only-3-million-in-net-expenses-so-far
Cybersecurity Dive. (2021). Marriott finds financial reprieve in reduced GDPR penalty. https://www.cybersecuritydive.com/news/marriott-finds-financial-reprieve-in-reduced-gdpr-penalty/588190/
Yahoo Data Breach Settlement. (2019). Yahoo data breach settlement. https://yahoodatabreachsettlement.com/
Federal Trade Commission. (2024). FTC takes action against Marriott-Starwood over multiple data breaches. https://www.ftc.gov/news-events/news/press-releases/2024/10/ftc-takes-action-against-marriott-starwood-over-multiple-data-breaches
Federal Trade Commission. (2019). Equifax data breach settlement. https://www.ftc.gov/enforcement/refunds/equifax-data-breach-settlement
SANS Institute. (2021). What you need to know about the SolarWinds supply chain attack. https://www.sans.org/blog/what-you-need-to-know-about-the-solarwinds-supply-chain-attack/
Touro University Illinois. (2021). The 10 biggest ransomware attacks of 2021. https://illinois.touro.edu/news/the-10-biggest-ransomware-attacks-of-2021.php The SSL Store. (2017). 2013 Target data breach settled. https://www.thesslstore.com/blog/2013-target-data-breach-settled/
NBC News. (2017). Target settles 2013 hacked customer data breach for $18.5 million. https://www.nbcnews.com/business/business-news/target-settles-2013-hacked-customer-data-breach-18-5-million-n764031
IT Governance. (2021). The 5 biggest ransomware payouts of all time. https://www.itgovernance.co.uk/blog/the-5-biggest-ransomware-pay-outs-of-all-time
BleepingComputer. (2021). Computer giant Acer hit by $50 million ransomware attack. https://www.bleepingcomputer.com/news/security/computer-giant-acer-hit-by-50-million-ransomware-attack/
CNN. (2021). JBS cyberattack and its impact on the global meat supply chain. https://www.cnn.com/2021/06/01/business/jbs-cyberattack-meat-shortage/index.html
BlackFog. (2021). The state of ransomware in 2021. https://www.blackfog.com/the-state-of-ransomware-in-2021/
BleepingComputer. (2021). Insurance giant CNA hit by new Phoenix CryptoLocker ransomware. https://www.bleepingcomputer.com/news/security/insurance-giant-cna-hit-by-new-phoenix-cryptolocker-ransomware/
ExtremeTech. (2021). Cyberpunk developer hit with ransomware attack. https://www.extremetech.com/gaming/319882-cyberpunk-developer-hit-with-ransomware-attack
ZDNet. (2021). Updated Kaseya ransomware attack FAQ: What we know now. https://www.zdnet.com/article/updated-kaseya-ransomware-attack-faq-what-we-know-now/
Acknowledgements
Special thanks to my talented publisher, Camille Sharon Kleinman; skilled editor, Shelly Zevlever; and meticulous analyst, Hesham Mashhour.